Chrome 154 Now Warns Before Opening Insecure HTTP Sites — Why You’re Seeing It and What to Do
Chrome 154 now warns by default before opening public sites that only support insecure HTTP. Here’s what the warning means, when to proceed and how HTTPS protects you.
Contents
- What changed in Chrome 154?
- What is the new warning protecting you from?
- What happens when you type an HTTP address?
- Does this affect every website without HTTPS?
- Is the site hacked if Chrome shows the warning?
- What should you do when the warning appears?
- Why is HTTP risky even if you are not typing a password?
- Why did Google wait until Chrome 154?
- Can you turn the warning off?
- What should website owners do?
- Will this affect SEO?
- HTTP vs HTTPS in simple terms
- Does the padlock mean a website is trustworthy?
- Why this matters on public Wi-Fi
- What if the warning appears on your router page?
- What about work and school networks?
- Could a captive portal trigger confusing warnings?
- How to check your Chrome version
- Does the change apply to Android too?
- A practical rule for users
- Frequently asked questions
- Why is Chrome suddenly warning that a site is not secure?
- Does the warning mean the site has malware?
- Can I continue to the site?
- Can I disable the warning?
- Why does my router still work over HTTP?
- Does HTTPS guarantee a site is trustworthy?
- The bottom line
- Sources
Last reviewed: October 11, 2026. If Chrome suddenly stops before opening a website and warns that the site does not support a secure connection, the browser may be doing exactly what Google intended.
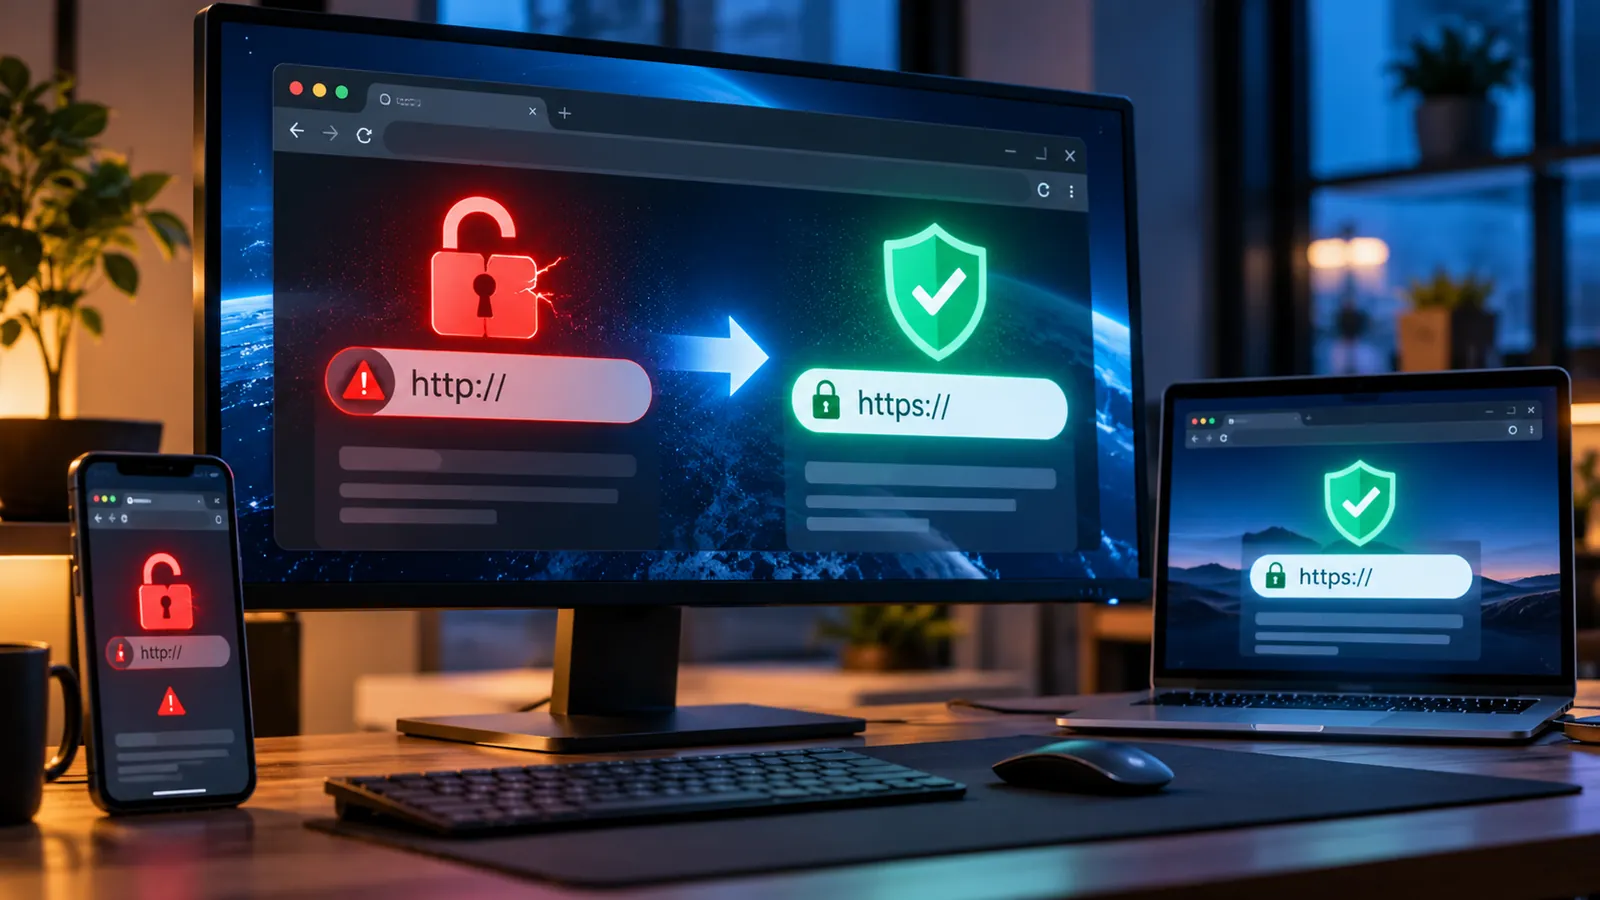
Chrome 154 turns on the public-site version of Always Use Secure Connections by default. That means Chrome can ask for your permission before the first visit to a public website that only supports unencrypted HTTP instead of HTTPS.
The change is designed to reduce the risk of attackers reading or modifying traffic while it travels between your browser and a website. It does not automatically mean the site is malware, hacked or fraudulent. It means the connection itself is not protected by HTTPS.
What changed in Chrome 154?
Google promoted Chrome 154 to the stable channel on September 22, 2026. The Chrome 154 release notes state that the browser now asks before connecting to a public site over an insecure HTTP connection by default.
Google announced this transition in advance as part of a broader move toward HTTPS-by-default browsing. The feature had already been enabled in more limited situations, including Enhanced Safe Browsing users, before becoming the normal default.
What is the new warning protecting you from?
HTTPS encrypts the connection between your browser and the website.
Without HTTPS, someone who can intercept traffic on the network path may be able to read data or modify the page before it reaches you.
That matters on public Wi-Fi, compromised routers, malicious networks and other environments where an attacker may be able to observe or tamper with unencrypted traffic.
An HTTP page can be legitimate and still be insecure. The warning is about the connection technology, not a verdict on the site owner’s intentions.
What happens when you type an HTTP address?
Chrome tries to use a secure connection where possible. If the public site supports HTTPS, the secure version should load normally.
If it only supports HTTP, Chrome 154 can display a warning before proceeding.
You can choose whether to continue, but Chrome deliberately adds friction so you do not enter an insecure public website without noticing.
Does this affect every website without HTTPS?
The default Chrome 154 behavior focuses on public sites.
Google defines these as sites with globally unique public names. The public-sites-only mode is designed not to warn for many local-network destinations, including common private IP ranges and short internal hostnames.
- 192.168.x.x router or device pages.
- 10.x.x.x private network addresses.
- Short internal names such as go/ used inside an organization.
This is intentional because routers, printers and other local devices often still use HTTP configuration pages and cannot always obtain normal public HTTPS certificates.
Is the site hacked if Chrome shows the warning?
No. The warning alone does not prove compromise.
It means Chrome could not establish an HTTPS connection to that public site.
Possible explanations include an old website that never added HTTPS, a broken certificate setup, an outdated HTTP bookmark, a redirect to an insecure destination or network interference.
You should still be cautious if the page asks for passwords, payment information, personal documents or other sensitive data.
What should you do when the warning appears?
- Check the address carefully for spelling mistakes.
- Try replacing http:// with https://.
- Search for the organization’s official website rather than relying on an old bookmark.
- If the page handles sensitive information and HTTPS does not work, do not enter passwords or payment details.
- Proceed to the HTTP version only if you understand the risk and genuinely trust the destination.
A simple informational page may be lower risk than a banking or login portal, but unencrypted content can still be modified in transit.
Why is HTTP risky even if you are not typing a password?
The risk is broader than stolen form data.
Because the connection is not protected end to end, an attacker in the network path may be able to alter content, inject scripts, replace downloads, insert advertising or redirect links.
HTTPS also helps the browser verify that it is communicating with the domain represented by the site’s certificate rather than an impostor on the connection path.
Why did Google wait until Chrome 154?
Google has moved toward HTTPS by default gradually to avoid breaking legitimate websites and local-network devices.
Chrome had already enabled related protections in Incognito and for Enhanced Safe Browsing users, and it prevented some HTTPS-to-HTTP downgrades before Chrome 154.
The staged approach gave website owners and IT departments time to migrate old public sites to HTTPS.
Can you turn the warning off?
Yes. Google says users can disable the warnings by turning off Always Use Secure Connections.
The option is generally under Settings > Privacy and security > Security.
For most users, leaving it enabled is the safer choice. If one legitimate old site causes trouble, fixing the site’s HTTPS support is better than weakening the browser globally.
What should website owners do?
If you run a public website that still depends on HTTP, the new Chrome behavior is a strong reason to finish an HTTPS migration.
- Install and renew a valid TLS certificate.
- Redirect HTTP URLs to HTTPS.
- Update internal links.
- Remove mixed-content images, scripts, fonts and APIs.
- Update canonical URLs and XML sitemaps.
- Test forms, downloads and old redirects.
Google specifically recommended that developers and IT professionals enable Always Use Secure Connections early to identify remaining sites that still depend on insecure HTTP.
Will this affect SEO?
A properly configured HTTPS site should not be harmed by the change.
The larger risk is keeping an important public site on HTTP. Users may abandon the page when Chrome interrupts access, and search engines have encouraged HTTPS deployment for years.
Website owners should make sure search engines and users both land consistently on the HTTPS version.
HTTP vs HTTPS in simple terms
HTTP transfers web traffic without the encryption layer provided by TLS.
HTTPS is HTTP protected by TLS, providing encryption, integrity protection and server authentication through digital certificates.
HTTPS does not guarantee that a site is honest. A phishing page can also use HTTPS. It protects the connection, not the intentions of the website operator.
Does the padlock mean a website is trustworthy?
No. A secure connection and a trustworthy business are two different questions.
HTTPS means the connection is encrypted and the certificate matches the domain under normal certificate rules. It does not mean the seller is legitimate, the information is accurate or the site cannot host harmful content.
You still need to check the domain name and context before entering sensitive information.
Why this matters on public Wi-Fi
The new behavior is especially useful on networks you do not control.
On coffee-shop, airport, hotel or other shared Wi-Fi, an unencrypted HTTP connection creates more opportunity for traffic interception or modification.
HTTPS protects the web session even when the underlying Wi-Fi network is not fully trusted.
That does not make public Wi-Fi completely risk-free, but it removes one major source of exposure.
What if the warning appears on your router page?
Chrome’s default public-sites-only mode is designed to avoid warnings for many private-network destinations such as 192.168.0.1 or 10.x.x.x.
If you still see a warning for a local device, check whether you are using a public hostname rather than a local IP, or whether the device is redirecting you elsewhere.
Do not install random certificates or browser extensions just to remove a security warning unless you understand exactly why the device requires them.
What about work and school networks?
Chrome administrators can control this behavior through enterprise policies.
Google documents policies such as HttpsOnlyMode and allow-list controls for organizations that still operate approved HTTP services.
A managed Chrome installation may therefore behave differently from a personal browser.
Could a captive portal trigger confusing warnings?
Yes. Hotels, airports and cafés sometimes redirect the first connection to a sign-in or terms page.
If the network intercepts the request before you are fully connected, Chrome can show unexpected security behavior.
Complete the network’s official captive-portal login, then revisit the destination. Never type an unrelated website password into the portal.
How to check your Chrome version
- Open Chrome.
- Open the three-dot menu.
- Go to Help > About Google Chrome on desktop.
- Chrome will check for updates.
- Relaunch if an update is installed.
Chrome 154 introduced the new HTTP warning default. If you are already using a later version such as Chrome 155, the protection still applies because browser releases normally carry forward security defaults.
Does the change apply to Android too?
Yes. Google’s Chrome 154 release notes describe the behavior across Android, ChromeOS, Linux, macOS, Windows and Fuchsia unless otherwise specified.
The exact design of the warning can differ between desktop and mobile, but the security principle is the same.
Android users who want a broader set of device protections can also read Android 17 Advanced Protection Adds 6 Powerful Security Features.
A practical rule for users
When Chrome warns about a public HTTP site, ask: Do I actually need to use the insecure version?
If HTTPS exists, use it. If the site requests sensitive information but cannot provide HTTPS, stop.
If it is a low-risk legacy page you genuinely trust and there is no secure alternative, Chrome still lets you make an informed choice instead of silently opening it.
Frequently asked questions
Why is Chrome suddenly warning that a site is not secure?
Chrome 154 enabled Always Use Secure Connections for public sites by default, so the browser now warns before visiting a public website that only supports HTTP.
Does the warning mean the site has malware?
No. It means the connection is not protected by HTTPS. The site could still be legitimate, but the traffic is easier to intercept or modify.
Can I continue to the site?
Chrome can allow you to proceed, but avoid entering sensitive information on an HTTP connection.
Can I disable the warning?
Yes, by turning off Always Use Secure Connections, but leaving it enabled is safer for most users.
Why does my router still work over HTTP?
Chrome’s public-site mode generally excludes private IP addresses and short local hostnames because many local devices cannot use normal public HTTPS certificates.
Does HTTPS guarantee a site is trustworthy?
No. HTTPS protects the connection; it does not guarantee that the website itself is honest.
The bottom line
Chrome’s new HTTP warning is not a random error. It is a deliberate security change that makes insecure public websites more visible.
If the warning appears, look for an HTTPS version first and avoid sending sensitive information over the insecure connection.
For website owners, the message is simple: public HTTP-only sites are now more likely to trigger friction in Chrome, so completing the move to HTTPS is increasingly important.
Sources
Chrome for Developers — Chrome 154 release notes.
Google Security Blog — HTTPS by default.
Chrome Releases — Chrome 154 Stable Channel Update.
Chrome Enterprise — release notes and HTTPS-only policy guidance.
You may also like
 Technology & How-To
Windows 11 Search Is Getting a Major Redesign — You Can Change Settings Directly From Search
Microsoft is testing a faster WinUI 3 Windows Search with inline actions that can change dark mode, Bluetooth,…
 Technology & How-To
NVIDIA Is Ending Windows 10 Game Ready Driver Support — What GeForce Users Need to Know
NVIDIA says October 2026 is the final month for full Windows 10 Game Ready and Studio Drivers. Here’s…
 Technology & How-To
Galaxy S24 Gets Android 17 / One UI 9 — New Features, Download Size and Rollout Status
Samsung has started rolling out stable One UI 9 based on Android 17 to the Galaxy S24 series,…