
Can Hackers See Which Websites You Visit on Public Wi-Fi? What HTTPS Actually Hides
Can a hacker or hotspot owner see which websites you visit? Understand HTTPS, DNS, ECH, VPNs, fake Wi-Fi hotspots, and how to protect your browsing on public networks.
Contents
- 1. The quick answer: what can someone see on public Wi-Fi?
- A practical visibility guide
- 2. How public Wi-Fi carries your internet traffic
- 3. What HTTPS protects, and why it changes the answer
- 4. Can the Wi-Fi owner see which websites you open?
- 5. DNS: why a website name can be visible before the page loads
- 6. SNI, TLS handshakes, and Encrypted Client Hello
- 7. Can someone on the same hotspot read your passwords or messages?
- 8. What changes when a website uses plain HTTP?
- 9. The difference between a normal hotspot and an “evil twin”
- 10. Can a fake hotspot bypass the padlock?
- 11. Can the hotspot operator see Google searches, YouTube videos, or messages?
- 12. Does Incognito or Private Browsing hide activity from Wi-Fi owners?
- 13. Does using a VPN stop public Wi-Fi monitoring?
- 14. VPN versus secure DNS versus HTTPS: what each one does
- 15. Does a Wi-Fi password make a network private?
- 16. Can hotel and airport Wi-Fi record browsing history?
- 17. Practical protection checklist before joining public Wi-Fi
- 18. How to improve Wi-Fi privacy on Windows 11
- 19. How to improve privacy on Android phones
- 20. How to improve privacy on iPhone, iPad, and Mac
- 21. What to do if a public Wi-Fi portal asks for personal information
- 22. Signs a hotspot might be suspicious—and what they really mean
- 23. What should you do if you already entered a password on a fake page?
- 24. Four realistic public Wi-Fi scenarios
- Scenario A: You open your bank's real HTTPS website
- Scenario B: You visit an old HTTP-only page
- Scenario C: You click a “hotel sign-in” link from a stranger
- Scenario D: You connect through a reputable full-tunnel VPN
- 25. Common misconceptions about public Wi-Fi privacy
- 26. The safest approach for everyday browsing
- Sources and further reading
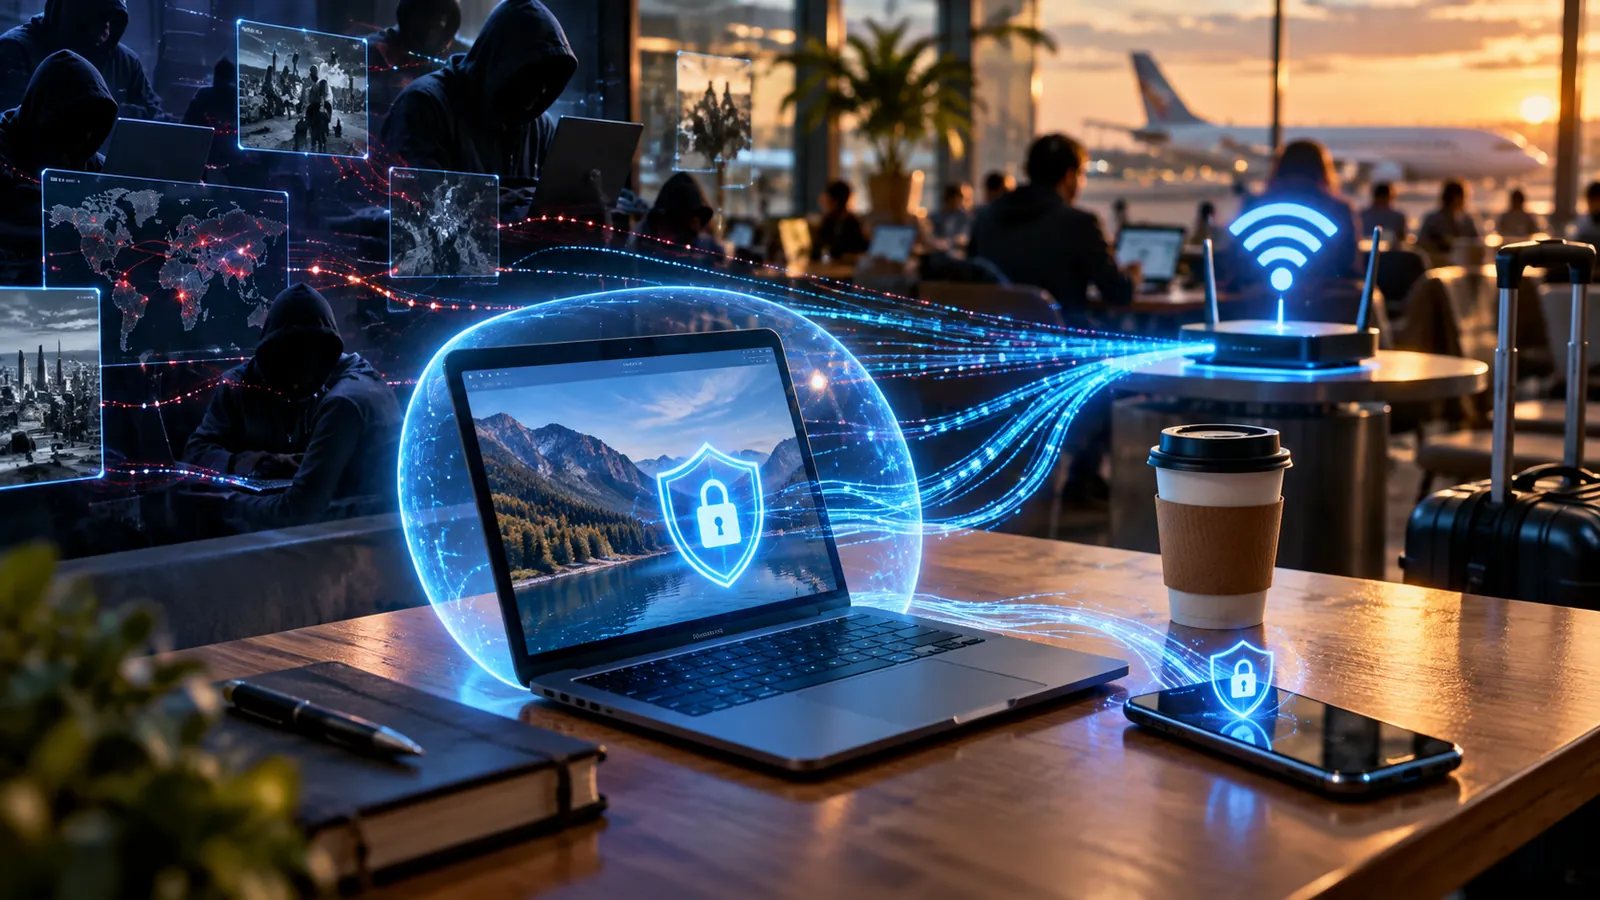
You connect to the free Wi-Fi at an airport, hotel, coffee shop, or shopping center. Your phone opens a familiar website, the browser reports a secure connection, and everything appears normal. But who else can see where you go online? Can the person operating the hotspot read your searches? Can somebody sitting nearby steal your passwords? And does a VPN actually make your browsing invisible?
The short answer is that a public Wi-Fi network can reveal some information about your internet activity, but it does not automatically reveal everything you read, type, or send. Modern HTTPS encryption protects the contents of most normal website connections. However, network operators and capable observers may still learn the destination of a connection from DNS requests, unencrypted TLS metadata, destination IP addresses, or other signals. Malicious hotspots create additional risks, especially when they trick you into entering information on a fake website.
The details matter because the difference between seeing the website’s name and reading what happens inside the website is enormous. This guide explains the distinction, the real risks, the safeguards that work, and what to do if you think a hotspot was malicious. It focuses on ordinary consumer devices rather than a specially managed work computer or a device already infected with spyware.
1. The quick answer: what can someone see on public Wi-Fi?
When a website uses HTTPS correctly and your device has not been compromised, other people on the network ordinarily cannot simply read the pages, passwords, messages, search terms, or forms exchanged inside that encrypted session. That includes the text you enter on a properly secured login page.
Nevertheless, a hotspot operator may be able to observe metadata: when your device connected, how much data it transferred, which IP addresses it contacted, and—in some configurations—which domain names it looked up or announced while establishing connections. A person on the same hotspot does not necessarily have access to all of those observations; network isolation, wireless encryption, permissions, and access to the router affect what that person can observe.
The US Federal Trade Commission makes an important point: widespread website encryption has made everyday public Wi-Fi use considerably safer than it was years ago. Public Wi-Fi is not inherently a guarantee of identity theft, and a Wi-Fi password is not proof that a hotspot operator is trustworthy.
A practical visibility guide
- Whether your device is connected: Generally visible to the access point. It knows that it is providing a connection to your device.
- How much data you send and receive: Often visible to the hotspot operator; connection timing and traffic volume are not normally hidden by HTTPS.
- Destination IP addresses: Usually visible to equipment routing your traffic. An IP address might serve multiple domains, so it is not always an exact website identifier.
- Website domain names: Sometimes visible through conventional DNS queries or unencrypted TLS server-name information; newer privacy features can reduce this exposure.
- A complete HTTPS page address, including its path and query: Normally encrypted. A local observer typically cannot distinguish
example.com/private-reportfromexample.com/public-pageby reading the HTTPS request itself. - Passwords, messages, files, and page content sent over HTTPS: Normally encrypted against passive local interception.
- Traffic to an unencrypted HTTP website: Potentially readable or modifiable by somebody who can intercept the traffic.
- Your whole browser history: Not automatically. A network administrator might reconstruct portions of activity from logs, but that is different from opening your browser’s local history.
These descriptions assume ordinary networking, not malware, an installed interception certificate, or a browser warning that the user has deliberately bypassed.
2. How public Wi-Fi carries your internet traffic
A Wi-Fi access point connects nearby devices to a local network and usually routes their traffic toward an internet connection. In a café, the business might own the router; in an airport, a network contractor might operate the service; in a hotel, traffic might pass through additional authentication and management systems.
Different parties therefore have different vantage points. The hotspot operator controls equipment that handles your connection. The internet provider handling the hotspot’s upstream service sees traffic at another point along its route. An ordinary customer connected to the same network may have only limited visibility, especially if the hotspot isolates devices from one another.
A useful analogy is a delivery service. Encryption can keep the contents of a parcel sealed, while the systems moving the parcel still need routing information. The destination address or the size of the parcel may tell an observer something; neither automatically reveals what is inside.
Even when the website is encrypted, your browser must make a series of technical connections. Some of the supporting information is visible unless additional privacy technologies are used. That is why two apparently contradictory statements—“HTTPS hides what you do” and “networks may know which sites you visit”—can both be partly true.
3. What HTTPS protects, and why it changes the answer
HTTPS is HTTP carried over Transport Layer Security, or TLS. It creates an authenticated, encrypted connection between a browser or application and the server it has reached. The server’s certificate helps the browser confirm that it is communicating with the expected destination, subject to the trust and certificate validation rules on the device.
With a correctly established HTTPS connection, outsiders along the network path cannot normally read the HTTP request path, page content, cookies, form values, or response data. They also cannot silently change an encrypted page without causing integrity checks to fail. This protection applies on public Wi-Fi just as it does on a home network.
The website’s identity still matters. A phishing site can use its own valid HTTPS certificate and show a secure connection indicator while stealing anything you willingly enter. HTTPS means the connection to that site is protected against interception; it does not mean the site itself is honest. The FTC explicitly warns that scammers can operate convincing encrypted websites.
In Chrome, you can review a site’s security information from the control beside its address. Chrome also offers an Always use secure connections setting that tries HTTPS and warns before opening sites that do not support a secure connection. See Google’s connection security guide and Chrome security settings.
4. Can the Wi-Fi owner see which websites you open?
Sometimes, yes—the domain or a strong clue to it. Being the owner or administrator of a network does not automatically grant access to the contents of a modern encrypted website, but it can make network-level metadata and logging available.
Suppose you open https://travel.example/booking/confirmation?reference=123. If the browser uses ordinary HTTPS, a network observer might learn that your device connected to travel.example from a DNS request or a TLS handshake. The observer normally does not obtain /booking/confirmation?reference=123 or the confirmation page’s contents just by inspecting that encrypted connection.
There are important exceptions and qualifications. If the browser uses encrypted DNS and the server supports Encrypted Client Hello, the site’s domain can be harder to observe. A destination IP address may still narrow the possibilities, and a dedicated server’s address may effectively reveal a site. Network timing and traffic patterns can sometimes support inferences, but those are not the same as a complete, trustworthy list of visited URLs.
An operator who requires you to authenticate to its Wi-Fi portal may also associate traffic metadata with your room number, voucher, email address, or account. Whether it actually does so depends on its system and privacy practices. Never assume that a hotspot is anonymous merely because access costs nothing.
5. DNS: why a website name can be visible before the page loads
Computers generally use the Domain Name System, or DNS, to translate names such as news.example into the IP addresses used for network connections. Traditionally, many DNS lookups were transmitted without encryption. A network operator able to observe those requests could learn which domains your device requested, even when the websites themselves used HTTPS.
There is a subtle point: a DNS query does not necessarily prove that you read a page. Apps, ads, background services, previews, malware scanners, and browser prefetching can request names without you intentionally visiting a site. Similarly, DNS caching can mean a website loads without a new observable DNS request.
DNS over HTTPS (DoH) and DNS over TLS (DoT) encrypt DNS queries between your device or browser and a compatible resolver. This protects the lookup from ordinary local observation, although the resolver itself still processes the query. It also does not hide the destination IP address or every other clue about your traffic.
Mozilla explains both conventional DNS exposure and DoH in its Firefox DNS over HTTPS documentation. Chrome offers a related Use secure DNS option, but automatic configurations may fall back to unencrypted lookup under some conditions. For maximum clarity, check the browser’s actual settings rather than assuming that all DNS traffic is encrypted.
6. SNI, TLS handshakes, and Encrypted Client Hello
A browser may connect to a server that hosts many websites on the same IP address. During the initial TLS handshake, it historically sent a field called Server Name Indication (SNI) so the server could select the appropriate certificate and site. In conventional TLS connections, that field is generally visible to a network observer.
This means encrypted page content and an exposed domain name can coexist. Encrypted Client Hello (ECH) is designed to improve this situation by encrypting sensitive portions of the initial TLS connection setup, including the true requested server name when supported by both client and server.
ECH is not a universal invisibility switch. The browser, DNS configuration, website hosting provider, and network environment all influence whether it is actually used. Some managed or filtered environments can change its behavior. Even with ECH, an observer may still see server IP addresses and traffic patterns. Mozilla’s ECH explanation documents these limitations and the relationship between ECH and secure DNS.
The takeaway is simple: on a modern connection, the question is no longer merely “Is the site HTTPS?” but also “How is the destination being resolved and how much connection metadata is exposed?” Ordinary users do not need to memorize the protocol details, but they should understand that secure page content and completely hidden site identity are different protections.
7. Can someone on the same hotspot read your passwords or messages?
If you submit a password to the real website over valid HTTPS, a passive eavesdropper on the same Wi-Fi network should not be able to read that password from the traffic. The same principle protects the body of webmail, direct messages, and other data transferred through properly secured connections.
That does not mean passwords are immune to every threat. Attackers can set up a fake login page, send phishing links, exploit a compromised application, or take advantage of a warning that a user ignores. A malicious browser extension or malware already installed on your own device can also capture information before encryption protects it.
What about apps? Most reputable mainstream apps use encrypted connections, but there is no universal guarantee that every app, embedded web view, or old device does so correctly. An application with insecure network requests might expose information even if the websites you visit in your browser are protected.
A good rule is to treat encryption as a strong defense against network eavesdropping, not as a substitute for checking the website name, using a password manager, installing updates, and enabling strong account authentication.
8. What changes when a website uses plain HTTP?
HTTP without TLS lacks the same end-to-end encryption and integrity protection. Someone in a position to intercept unencrypted traffic may be able to read its contents or alter the response. On an untrusted network, that might include text on the page, links, requests, or information submitted through an insecure form.
Modern browsers increasingly attempt to use HTTPS and warn about insecure pages, which reduces exposure. But older devices, local web interfaces, specialty sites, and badly configured services can still use plain HTTP. A warning labeled Not secure deserves attention, especially if the site asks for credentials, payment information, or personal details.
Do not type private information into an HTTP form. If the page has an HTTPS version, navigate directly to that address. If the site unexpectedly switches to HTTP during sign-in, stop rather than assuming the earlier secure page protects the next one.
There is also a distinction between an ordinary captive portal and a malicious form. A legitimate hotspot may display a simple local terms page over HTTP to begin a login flow. That situation should never be mistaken for permission to enter banking passwords or email account credentials on an insecure page.
9. The difference between a normal hotspot and an “evil twin”
An evil twin is an attacker-controlled wireless network designed to resemble one that people expect to trust. A traveler might see a name resembling the airport’s official Wi-Fi or a hotel’s guest network and connect without checking which one is genuine.
The attacker may then control DNS responses, show deceptive portal pages, or direct visitors toward phishing sites. This does not magically break modern TLS: properly validated HTTPS will still resist ordinary interception. Instead, criminals often rely on confusion, impersonation, outdated software, and the user’s willingness to ignore a browser warning or enter details into the wrong page.
A hotspot can also be legitimate yet poorly secured. Weak administrator credentials, obsolete equipment, or inadequate separation between guest devices may create additional exposure. Conversely, even a completely open hotspot can carry safe HTTPS sessions. The distinction is about the security of each layer, not a single label such as “free” or “password protected.”
Before connecting, confirm the exact official network name with staff or the venue’s displayed instructions. Be especially cautious about similarly spelled networks and unexpected demands to install certificates, profiles, browser extensions, or “security apps” merely to browse.
10. Can a fake hotspot bypass the padlock?
A fake access point can relay traffic and attempt to interfere with connections, but it should not be able to present itself as a genuine HTTPS website without the appropriate certificate or another trust failure. A browser may block the connection with a certificate warning or a message such as Your connection is not private.
Do not dismiss such warnings as an ordinary inconvenience. Sometimes they result from incorrect device time, a captive portal, a genuine site misconfiguration, or security software. On an unfamiliar network, they can also be a sign that a connection is being intercepted. The safest response is to stop, disconnect, and investigate rather than clicking through to a sensitive site.
A more deceptive approach is to send you to a different domain controlled by the attacker. That fake domain may have valid HTTPS and therefore show a secure connection without being the real bank or service. Always examine the complete domain carefully, especially before logging in.
For public Wi-Fi portals, use the sign-in flow offered by the operating system or venue. Avoid installing a root certificate or device-management profile at the request of an unexpected portal; such changes can have consequences well beyond that Wi-Fi session.
11. Can the hotspot operator see Google searches, YouTube videos, or messages?
For a conventional encrypted web search, the text you type and the resulting pages are normally part of the encrypted HTTPS exchange. A network observer generally cannot read the exact search query directly from that traffic. However, it may learn that you contacted a search provider and may infer some activity from timing and volume.
The same general distinction applies to encrypted video services: a router may see connections, approximate traffic volume, and possibly a service domain, but that does not necessarily reveal the exact video title or what you typed into the search bar. Specialized traffic analysis can sometimes make educated guesses; it should not be confused with routinely reading every video URL.
Encrypted messaging services require extra nuance. Transport encryption protects information in transit, while end-to-end encryption, where provided and correctly implemented, is designed so that even the messaging service cannot read message contents in the ordinary course. Messaging metadata and account information may follow different rules. A Wi-Fi observer’s visibility should not be conflated with what the app provider itself collects.
Finally, a website you visit still sees its own interactions with you. HTTPS prevents outsiders from reading the exchange; it does not conceal that information from the receiving website or from somebody who controls your account.
12. Does Incognito or Private Browsing hide activity from Wi-Fi owners?
No. Incognito and Private Browsing primarily change what is stored locally in the browsing session, such as ordinary history or certain cookies after the private session ends. They do not inherently encrypt DNS requests, reroute internet traffic, or prevent a network operator from seeing available traffic metadata.
Using a private tab does not make a browser anonymous to the hotspot owner, the internet provider, the websites visited, or an organization administering the device. The exact behavior varies by browser, but privacy mode should never be confused with a VPN or with HTTPS.
Private browsing can be useful when temporarily using a shared device, although it cannot remove evidence held by websites, routers, account providers, or the operating system. If privacy from the local network is your goal, look to the actual network protection layers instead.
13. Does using a VPN stop public Wi-Fi monitoring?
A reputable, properly configured virtual private network (VPN) can add useful protection. Instead of connecting separately to websites in a way the local network can inspect, your device establishes an encrypted tunnel to a VPN server and routes the selected traffic through it.
For a full-tunnel setup with functioning DNS protection, a local hotspot operator will generally see a connection to the VPN endpoint and some metadata, but not the individual domain lookups and website destinations carried inside that tunnel. This is especially useful if you work remotely, require access to company systems, or want less visibility for the local network.
A VPN is not invisibility or automatic anonymity. The VPN provider may be in a position to observe connection metadata or activity, depending on how the service operates. Websites can still identify signed-in accounts, browser fingerprints, and tracking cookies. Malware and phishing remain possible. Misconfigured split tunneling, DNS leaks, or traffic outside the VPN may expose more than expected.
Choose a provider you trust, keep the app updated, and understand whether its protection applies to the entire device or only one browser. For many routine tasks over validated HTTPS, you do not need to purchase a VPN simply because you are using Wi-Fi at a café. Cloudflare’s explanation of VPN architecture and its limitations provides useful background.
14. VPN versus secure DNS versus HTTPS: what each one does
The three technologies solve different problems, and none replaces the others completely.
- HTTPS: Protects the contents and integrity of an authenticated connection to a website or service. It normally does not conceal all destination metadata from the network.
- Secure DNS (DoH or DoT): Encrypts name lookups between your device or application and the chosen resolver. It does not automatically hide the destination IP address or the ordinary TLS server name.
- Encrypted Client Hello (ECH): Helps conceal the requested server name in the TLS connection setup when the necessary browser and server support are present. It does not conceal every observable aspect of the connection.
- VPN: Tunnels selected device traffic to a separate endpoint and can substantially reduce what the local Wi-Fi network sees, but shifts an element of trust to the VPN service.
- Private browsing: Changes local history and session handling; it is not a network privacy mechanism.
- Private Wi-Fi or randomized MAC address: Reduces persistent device identifier tracking across networks. It does not encrypt website traffic or hide visited sites by itself.
The best combination depends on your goals. If you want to prevent a nearby opportunist from reading account data, correctly validated HTTPS already does much of the work. If you want to reduce which domains a venue can log, secure DNS plus effective ECH or a properly configured VPN may offer added privacy. If you want to avoid account phishing, neither one substitutes for verifying the address.
15. Does a Wi-Fi password make a network private?
Not necessarily. A password can mean that the wireless connection is protected with WPA2 or WPA3, which encrypts data on the local wireless link. That is valuable, but it does not automatically stop the access point’s own operator from recording available metadata or sending users to a malicious portal.
On a widely shared guest network, numerous visitors may know the same password. The security available to individual devices depends on the Wi-Fi protocol, network configuration, and isolation between clients. Being asked to enter a password is not a guarantee that you are on the venue’s authentic network.
Conversely, an open network does not strip the encryption from HTTPS. A correctly secured website can still protect data while it traverses an open hotspot. It is better to evaluate the security of the wireless link and the website connection as separate layers.
Where available, prefer modern, legitimate, well-administered networks and avoid obsolete security modes. But whether a site is genuine and uses HTTPS remains essential regardless of the Wi-Fi network’s name or lock symbol.
16. Can hotel and airport Wi-Fi record browsing history?
A hotspot management system may maintain connection logs and technical records, such as device identifiers, assigned IP addresses, connection times, traffic volume, and network destinations. In some environments, it can also record ordinary DNS requests or collect information from a sign-in portal.
These records are not identical to the browser history stored on your phone or laptop. They can be incomplete, may include background traffic you never intentionally initiated, and may omit page-level details from encrypted connections. The amount recorded depends on the hotspot’s architecture, logging policy, and applicable rules.
If you use your room number, email address, or a social sign-in to access the Wi-Fi, those identifiers could be associated with the session. Review any relevant portal privacy notice if you are concerned about data collection, and avoid providing unnecessary personal details to unexpected pages.
Public Wi-Fi is rarely the best place to assume complete anonymity. For particularly sensitive work, consider a personal mobile hotspot, a trusted VPN, or a network approved by your employer.
17. Practical protection checklist before joining public Wi-Fi
Use this short routine before you begin browsing:
- Confirm the real network name. Ask the venue directly, especially when several similar hotspots appear.
- Keep the device updated. Security updates improve protection against browser, operating-system, and wireless vulnerabilities.
- Avoid unexpected installations. Do not install certificates, configuration profiles, or browser extensions merely because a portal demands them.
- Use HTTPS. Check the actual site address and stop if a sensitive page reports that its connection is not private.
- Turn on multifactor authentication. Strong sign-in protection limits damage if a password is stolen through phishing or another method.
- Avoid automatic reconnection to unknown networks. Reconnect deliberately and remove hotspots you no longer need.
- Use a trusted VPN when your risk or privacy needs justify one. Confirm that it is connected before beginning sensitive work.
- Prefer your own cellular hotspot when convenient for high-risk activity. This removes the public venue’s network from the route, although your cellular provider still handles connectivity.
A well-maintained phone using legitimate HTTPS services is not automatically unsafe just because its Wi-Fi signal comes from a public hotspot. The practical goal is to avoid unnecessary exposure and obvious traps, not to panic about every shared network.
18. How to improve Wi-Fi privacy on Windows 11
If you use a Windows laptop in airports, libraries, or hotels, set unfamiliar connections to a Public network profile. According to Microsoft’s network settings documentation, this profile reduces discoverability compared with the Private setting, which is designed for trusted local sharing.
- Open Settings and choose Network & internet.
- Select Wi-Fi, then open the properties for the current connection.
- Under Network profile type, choose Public network for an untrusted hotspot.
- Review Advanced sharing settings and keep network discovery and file or printer sharing off where they are not needed.
- In Chrome, open Settings → Privacy and security → Security and consider Always use secure connections and Use secure DNS.
- Disconnect from the hotspot when finished and remove it from remembered networks if you do not plan to return.
Menus can vary across Windows and browser versions. Do not switch an unfamiliar network to Private just to make a device visible; doing so is usually unnecessary for everyday internet access.
19. How to improve privacy on Android phones
Android’s exact menus depend on the phone manufacturer and version, but the core steps are similar. First, open Settings → Wi-Fi or Network & internet → Internet, select the connected network, and check its details. Confirm that the name matches the venue’s legitimate hotspot.
In Chrome for Android, open Settings → Privacy and security and look for Always use secure connections and secure DNS settings where available. Google documents HTTPS-only protection for Chrome on Android. Do not ignore a certificate error when logging in to a bank or email account.
Use a randomized MAC address or the phone’s equivalent privacy feature when supported. That can make long-term tracking of the device identifier more difficult, but it does not by itself hide domains or encrypt website content. Turn off automatic joining for unfamiliar networks and use the Forget option after visiting a hotspot you will not need again.
If the phone offers Private DNS, understand that it usually concerns DNS-over-TLS resolution, not a device-wide VPN. A browser may manage DNS separately. These privacy measures overlap but have different purposes.
20. How to improve privacy on iPhone, iPad, and Mac
On an iPhone or iPad, open Settings → Wi-Fi, tap the information control beside the hotspot, and review Auto-Join, Private Wi-Fi Address, and Forget This Network where offered. Apple recommends keeping private Wi-Fi addressing enabled on networks that support it; this reduces the ability to track the same hardware identifier across different networks. Read Apple’s private Wi-Fi address guide for details.
If you have iCloud+, iCloud Private Relay can provide additional privacy for covered Safari browsing by separating certain identifying information from browsing destinations. It is not the same as a general-purpose full-device VPN, and its availability and behavior can depend on the region, network, and settings. Apple’s Private Relay documentation explains the distinction.
On a Mac, review Wi-Fi network details, sharing options, and any installed VPN configuration. Use your browser’s secure-connection settings and keep software updated. As with Android and Windows, the most important habit is avoiding fake login pages and respecting certificate warnings.
21. What to do if a public Wi-Fi portal asks for personal information
Not every captive portal is malicious. Hotels and airports often ask visitors to accept terms, enter a voucher, or confirm access details before providing connectivity. However, a Wi-Fi sign-in page asking for your main email password, banking password, card PIN, or device management permissions is a serious warning sign unless you independently verify a legitimate reason and the correct service.
Compare the network name and portal branding with information obtained directly from the venue. If the portal unexpectedly redirects to an unrelated domain, displays spelling mistakes, requests payment details out of context, or insists that you disable browser security, disconnect instead of proceeding.
Captive portals can interfere with secure connections before you have signed in. A legitimate system may ask you to open a basic browser page to complete the network login; it should not require you to bypass a certificate warning on a sensitive website. Google explains how browser errors and portal sign-ins interact in its connection troubleshooting guide.
If in doubt, disable Wi-Fi and use mobile data while confirming the venue’s instructions. The inconvenience is small compared with exposing a primary account credential to an impersonator.
22. Signs a hotspot might be suspicious—and what they really mean
Certain patterns deserve investigation: multiple near-identical network names, repeated unexpected sign-in requests, requests to install a security certificate, forced visits to unrelated domains, and browser certificate errors that begin only on one particular network.
However, none of these signs alone proves that somebody is spying. A legitimate hotspot might have a broken login portal, an expired certificate, or a temporary configuration problem. Likewise, a completely smooth browsing experience is not proof that the network is authentic.
Avoid drawing conclusions from a single clue. Instead, stop entering sensitive information, check the venue’s official network name, switch to mobile data if necessary, and update your device. If you suspect a phishing portal, record the website address and report it to the venue’s IT or support team rather than continuing to test it with real passwords.
23. What should you do if you already entered a password on a fake page?
Act promptly, but work methodically. Disconnect from the suspicious hotspot and use a trusted connection, such as your cellular network or home internet, for account recovery.
- Change the exposed password directly through the real service’s official app or a manually typed, verified address.
- Change reused passwords elsewhere if the same password was used for multiple accounts. Each important account should have a unique password.
- Review recent sign-ins and active sessions using the account’s security page. Sign out unfamiliar devices where the service supports it.
- Enable multifactor authentication or passkeys, favoring phishing-resistant methods when they are available.
- Contact your bank immediately if payment information or authorization codes may have been exposed. Follow its fraud-reporting process and monitor transactions.
- Check for unusual apps, profiles, or certificates if the hotspot instructed you to install something. Seek qualified help before removing business-managed components.
- Run security updates and a trusted device scan if you suspect downloaded malware, not merely a fake web page.
- Preserve useful evidence, such as the suspicious domain and any messages, without posting your private credentials publicly.
Simply clearing browser history does not revoke stolen passwords or recover a compromised account. Likewise, installing a VPN after the incident cannot retroactively protect information already given to an attacker.
24. Four realistic public Wi-Fi scenarios
Scenario A: You open your bank’s real HTTPS website
You verified the domain and the browser shows a valid secure connection. A passive local network observer cannot ordinarily read the banking session’s password, account balance, or transfers. The venue might still observe connection metadata. This is a much safer situation than a sensational headline suggesting every public hotspot exposes online banking.
Scenario B: You visit an old HTTP-only page
Because the page lacks HTTPS, an observer who can intercept the relevant traffic may read or modify it. Even if the page is harmless, avoid entering any private data. Prefer its HTTPS equivalent or leave the site.
Scenario C: You click a “hotel sign-in” link from a stranger
The page may be an attacker-controlled lookalike. It can use HTTPS and still collect credentials that you type voluntarily. The correct response is to verify the Wi-Fi instructions with the hotel, not to trust a padlock in isolation.
Scenario D: You connect through a reputable full-tunnel VPN
The local network typically sees encrypted traffic to the VPN server rather than a list of individual browsing destinations within the tunnel. However, the VPN provider may see metadata, and websites still see interactions and logged-in accounts. You gain one layer of privacy without becoming untraceable.
25. Common misconceptions about public Wi-Fi privacy
Myth: Anyone sharing Wi-Fi can automatically read all my passwords. Not when those credentials are submitted over properly authenticated HTTPS. Phishing and insecure applications are separate concerns.
Myth: HTTPS hides every detail of the website I visit. It protects page contents and complete request paths, but destination metadata may remain observable depending on DNS and TLS privacy features.
Myth: A lock or secure-connection indicator means the website is legitimate. A criminal website can have a valid certificate. Check the actual domain and the nature of the request.
Myth: Incognito stops routers from keeping logs. Incognito primarily changes local browser behavior, not what a network can observe.
Myth: A VPN makes me anonymous to everyone. A VPN can reduce local network visibility, but it cannot hide your signed-in identity from a site or make phishing harmless.
Myth: A password-protected guest network is automatically safe. Wireless encryption is useful, but it does not establish trust in the router operator or every portal reached through that network.
Myth: If somebody knows a site’s IP address, they always know exactly which page was opened. IP addresses can host many sites; knowing an address is not the same as reading a full URL or page content.
26. The safest approach for everyday browsing
For most people, public Wi-Fi safety is about layered habits rather than an expensive collection of security products. Keep devices and browsers updated. Prefer sites and apps that use modern encryption. Verify the domain before signing in. Use unique passwords or passkeys, and protect accounts with multifactor authentication.
When joining an unfamiliar hotspot, verify the correct network name and reject unexpected certificate or installation prompts. For a laptop, use a public network profile and avoid exposing unnecessary local services. On a phone, enable private Wi-Fi addressing where appropriate and forget old guest networks that should not reconnect automatically.
If you need stronger privacy from the hotspot operator—or access to sensitive company resources—a trustworthy, correctly configured VPN or a personal cellular hotspot can be a reasonable addition. Remember that secure DNS and Encrypted Client Hello help protect different metadata and depend on support and settings.
The most accurate way to describe the risk is this: public Wi-Fi can reveal clues about where you connect, but a correctly authenticated HTTPS connection generally keeps what you do inside that connection unreadable to a passive observer. The largest avoidable risks often come from fake networks, phishing pages, insecure websites, ignored browser warnings, and poorly protected devices rather than from ordinary encryption suddenly failing in a café.
Sources and further reading
- US Federal Trade Commission — Are Public Wi-Fi Networks Safe?. Consumer advice explaining the protection HTTPS provides and the remaining need to recognize scams.
- Google Chrome Help — Check if a site’s connection is secure. Official guidance on HTTPS indicators, insecure pages, and certificate warnings.
- Google Chrome Help — Manage Chrome safety and security. Instructions for secure connections and secure DNS settings.
- Mozilla Support — Firefox DNS over HTTPS. Explanation of DNS privacy, encryption, and browser controls.
- Mozilla Support — Understand Encrypted Client Hello. Explanation of ECH and its relationship with DNS privacy.
- Microsoft Support — Essential network settings and tasks in Windows. Guidance on public network profiles and discoverability.
- Apple Support — Use private Wi-Fi addresses on Apple devices. Device identifier privacy and network settings.
- Apple Support — About iCloud Private Relay. Scope of Safari browsing protection and relay architecture.
- Cloudflare — What is a VPN?. Explanation of encrypted tunnels and trust considerations.
You may also like
 Technology & How-To
Can’t Copy Text from a PDF? Fix Scans, Restrictions and Garbled Text
Find out why PDF text will not copy, then choose the right fix for scans, copying restrictions, garbled…
 Technology & How-To
USB Works on PC but Not on TV? How to Find the Cause
Diagnose a USB drive that works on a computer but not a TV. Separate detection, missing files and…
 Technology & How-To
WhatsApp “Waiting for This Message”: Fixes for iPhone, Android and Web
Fix WhatsApp’s waiting-message notice by comparing your phone and linked devices, checking updates and protecting existing chat data.